When the CVE Lands, It’s Too Late
Istio ships a minor release every three months. Sounds predictable.
- Date
- Topic
- Lifecycle
- Reading time
- 2 min
- Version
- Translation
Istio ships a minor release every three months. Patches come more often, usually without much effort. Sounds predictable.
Figure as text
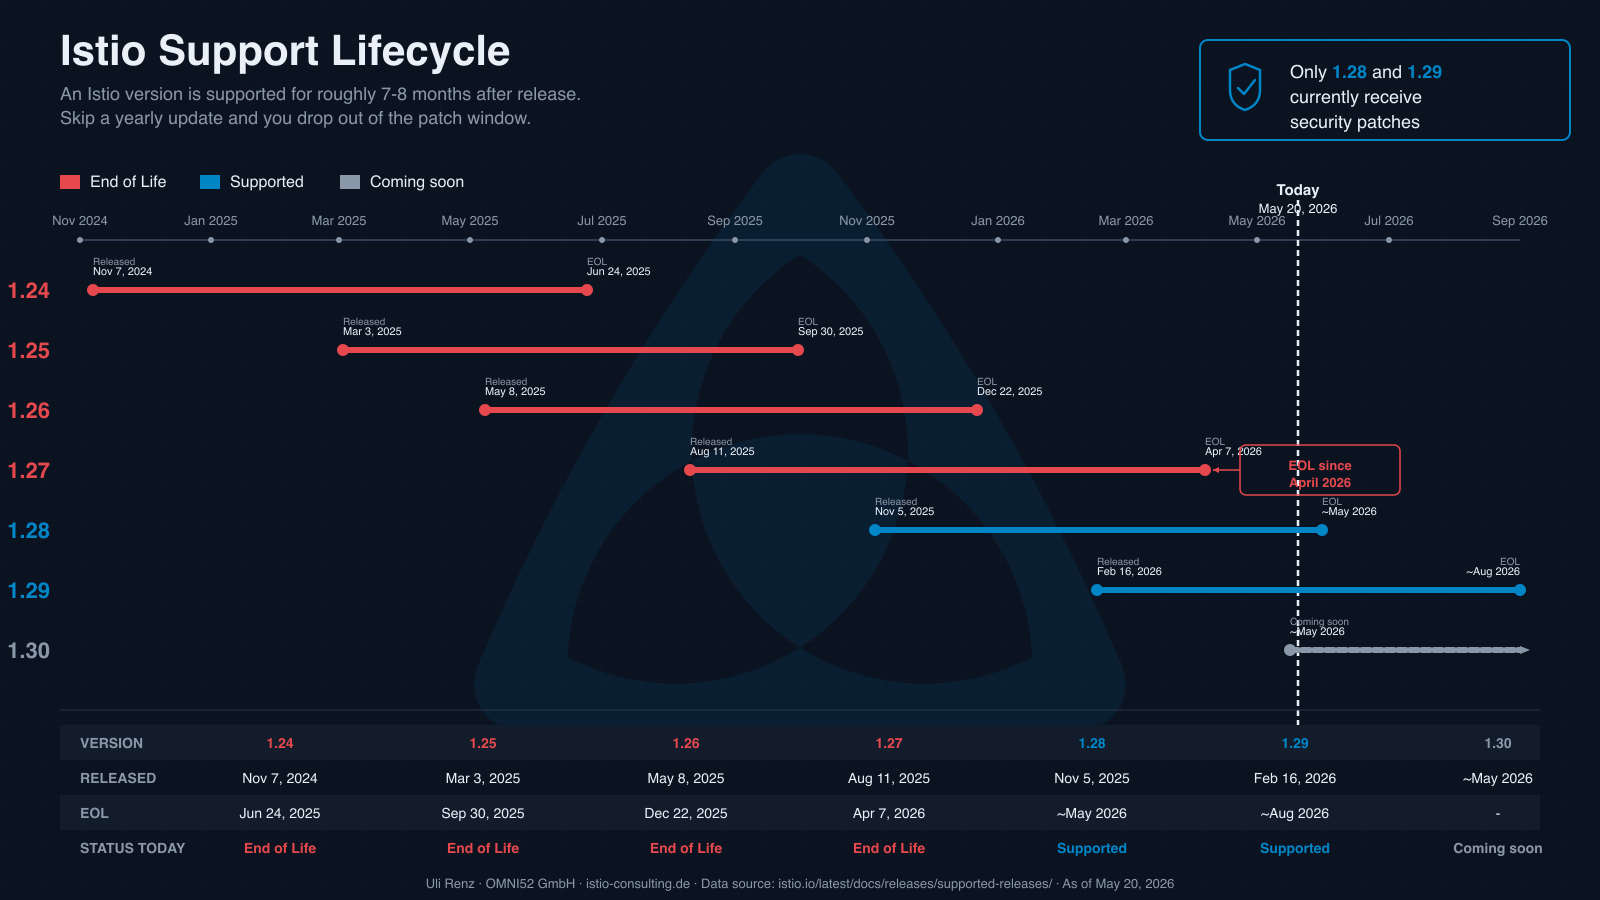
Timeline of the Istio support lifecycle for versions 1.24 through 1.30 with release and end-of-life dates, as of May 20, 2026. Only 1.28 and 1.29 receive security patches at that point: skip a year of updates and you fall out of the patch window.
In reality, I regularly see setups that have been sitting on the same minor version for 18 months. The reasoning: “An update is too risky, we’ll do it when we have time.”
That time never comes. It gets taken, usually at the moment nobody has any left.
The typical sequence:
A critical CVE gets published. A patch is available, but only for the last two minor versions. Your setup is five releases behind. Suddenly the question is no longer “update when it fits,” but “update by Friday, or compliance shows up at your door.”
What was justified as a controlled risk turns into an unplanned emergency migration across five version jumps within 24 hours. With everything that comes with it: breaking changes nobody has tested. API deprecations that happened along the way. Behavior changes in production traffic that show up in no changelog.
Patches are mostly painless. But when a CVE lands, the building is on fire and nobody brought a bucket.
That’s not an Istio problem. It’s a lifecycle problem.
What’s missing in most setups:
An established process for quarterly updates that isn’t reinvented every single time. A parallel installation or canary cluster that development teams can test their services against before the update goes to production. A clear understanding of which of your own configurations and CRDs stay compatible across versions and which don’t.
What I see instead: updates get treated like a project that starts from scratch every quarter. Discussion, risk assessment, postponement, eventually frustration, then nothing. That works right up until it doesn’t.
If you run Istio in production, you have a quarterly lifecycle problem. Whether you want to admit it or not. Everyone needs updates. The question is whether your process holds up when a CVE suddenly takes the choice away.
If you don’t have a working process, you don’t have an update problem. You’re sitting on a compliance problem that nobody has triggered yet.
Which topics would actually help you in this series? Lifecycle, debugging, architecture, multi-tenancy: drop it in the comments and it will feed into the coming weeks.